Cybersecurity & Data Privacy

Cyber Security & Data Privacy

STA - AIMS AUDITOR

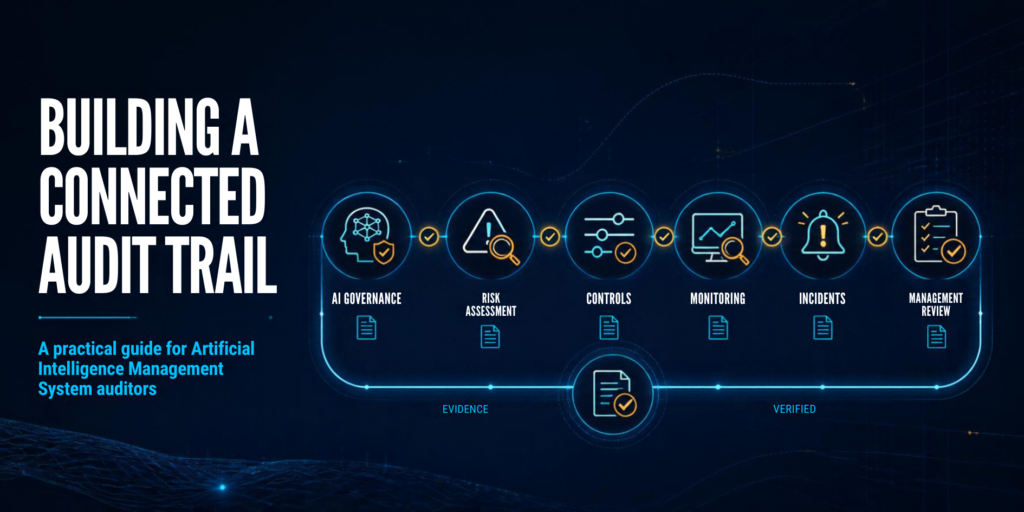
Building a Connected Audit Trail: A Practical Guide for AIMS Auditors

Why “connected” evidence matters more in AIMS audits than in most management systems ? Auditors moving into ISO/IEC 42001 conformity work from a background in ISO 9001, ISO 27001, or ISO 14001 will recognise the underlying Plan-Do-Check-Act structure immediately: internal audit under clause 9.2, management review under clause 9.3, and nonconformity and corrective action under […]

Building a Connected Audit Trail: A Practical Guide for AIMS Auditors Read More »
STA - Cyber Trust Mark Explained

Singapore-cyber-trust-mark-ss-712-2025-tiers

What SS 712:2025 Requires at Each Tier ? Why the Cyber Trust mark now sits at the centre of Singapore’s cybersecurity strategy ? For several years, Singapore’s Cyber Security Agency (CSA) offered two voluntary marks: Cyber Essentials for smaller organisations and Cyber Trust for larger, more digitally mature ones. In 2025, CSA enhanced both marks

Singapore-cyber-trust-mark-ss-712-2025-tiers Read More »